Dark Web Monitoring: Coverage, Evidence and Useful Responses
Dark web monitoring matches authorized identifiers against selected exposure sources and notifies you about findings. It can support account protection and incident response, but it does not see every private source, prevent every breach or remove all stolen copies. Its value depends on the evidence an alert supplies and the response you can perform.
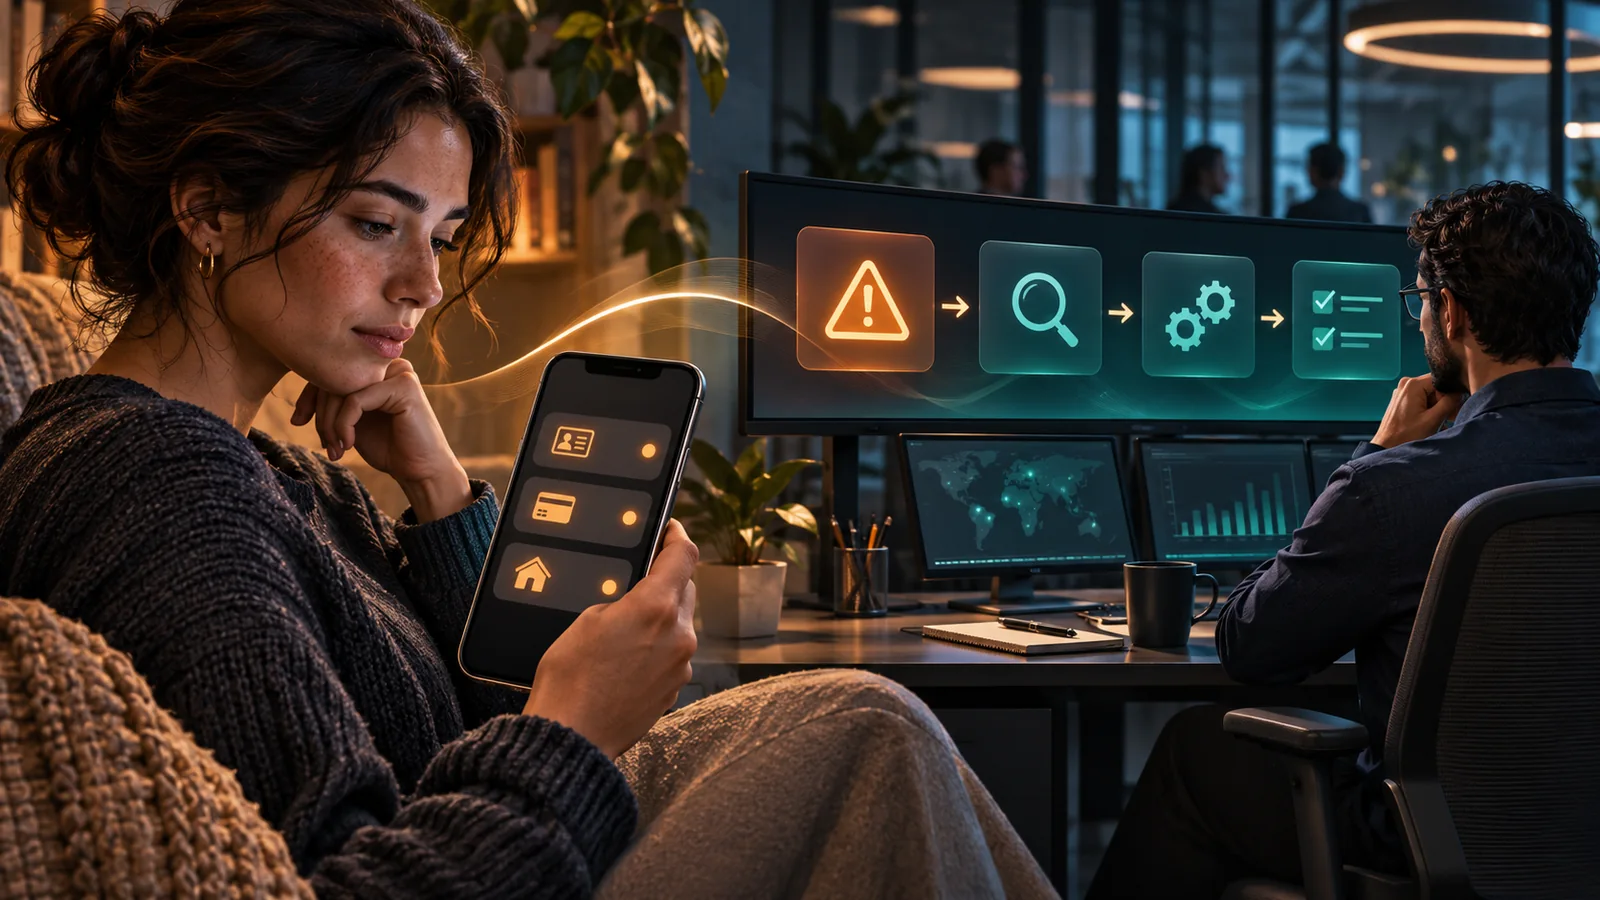
From collected record to response
Define the watchlist
Specify the personal identifiers or verified business domains you are authorized to monitor. A broad product name does not establish which assets your plan covers.
Collect and match
A provider processes available sources and matches fields against that watchlist. Data quality, access and parsing affect what can be found.
Assess the result
A finding needs context: the affected service, record type, available dates and whether it duplicates a previously handled exposure.
Act and document
Assign someone to investigate and use supported account, endpoint or financial controls. Preserve enough evidence to distinguish a later repost from a new incident.
Coverage is a specific claim
Known-breach lookups, infostealer records, public pastes and restricted forums are different source categories. A provider should explain which it covers rather than treating “the dark web” as one searchable database. Vendor documentation describes that vendor’s access, not a universal capability.
HIBP documents particular breach and stealer-log services; Flare describes collection categories and event processing. These are useful starting points for asking what fields an actual alert contains. Neither a high record count nor a polished dashboard establishes that your most important exposure will be found.
Questions an actionable alert should answer
| Subject | Why it matters | Useful caution |
|---|---|---|
| Which asset matches? | Routes the finding to an owner | An old identifier can still match |
| What was exposed? | Distinguishes a password from general identity data | Fields can be incomplete |
| Which date is shown? | Helps assess urgency and history | Detection is not necessarily infection time |
| Is it a repeat? | Avoids treating a repost as a new event | Changed evidence can still warrant review |
Pay for a response you can use
If all you need is a known-breach email check, a free lookup may answer that narrow question. A business may instead need domain verification, integrations, controlled evidence access and an analyst workflow. A household may value recovery assistance. These are separate reasons to pay.
If repeated alerts leave you wondering whether anything changed, ask for source dates and duplicate handling. More notifications do not necessarily mean more protection. A useful service helps you decide what action remains outstanding, while routine account security continues independently of its findings.
Questions people ask
Sources
Further reading
Glossary
Terms in this guide
Continue learning