Can Police Track VPN Users? Evidence and Limits
Yes, police may identify someone who uses a VPN, but a VPN connection does not automatically reveal a person’s identity or guarantee that useful logs exist. Identification can involve provider records, destination accounts, device evidence or other investigative leads. A legal request cannot recover records that were never retained. The evidence, provider practices and applicable legal process matter in each case.
Understanding the question
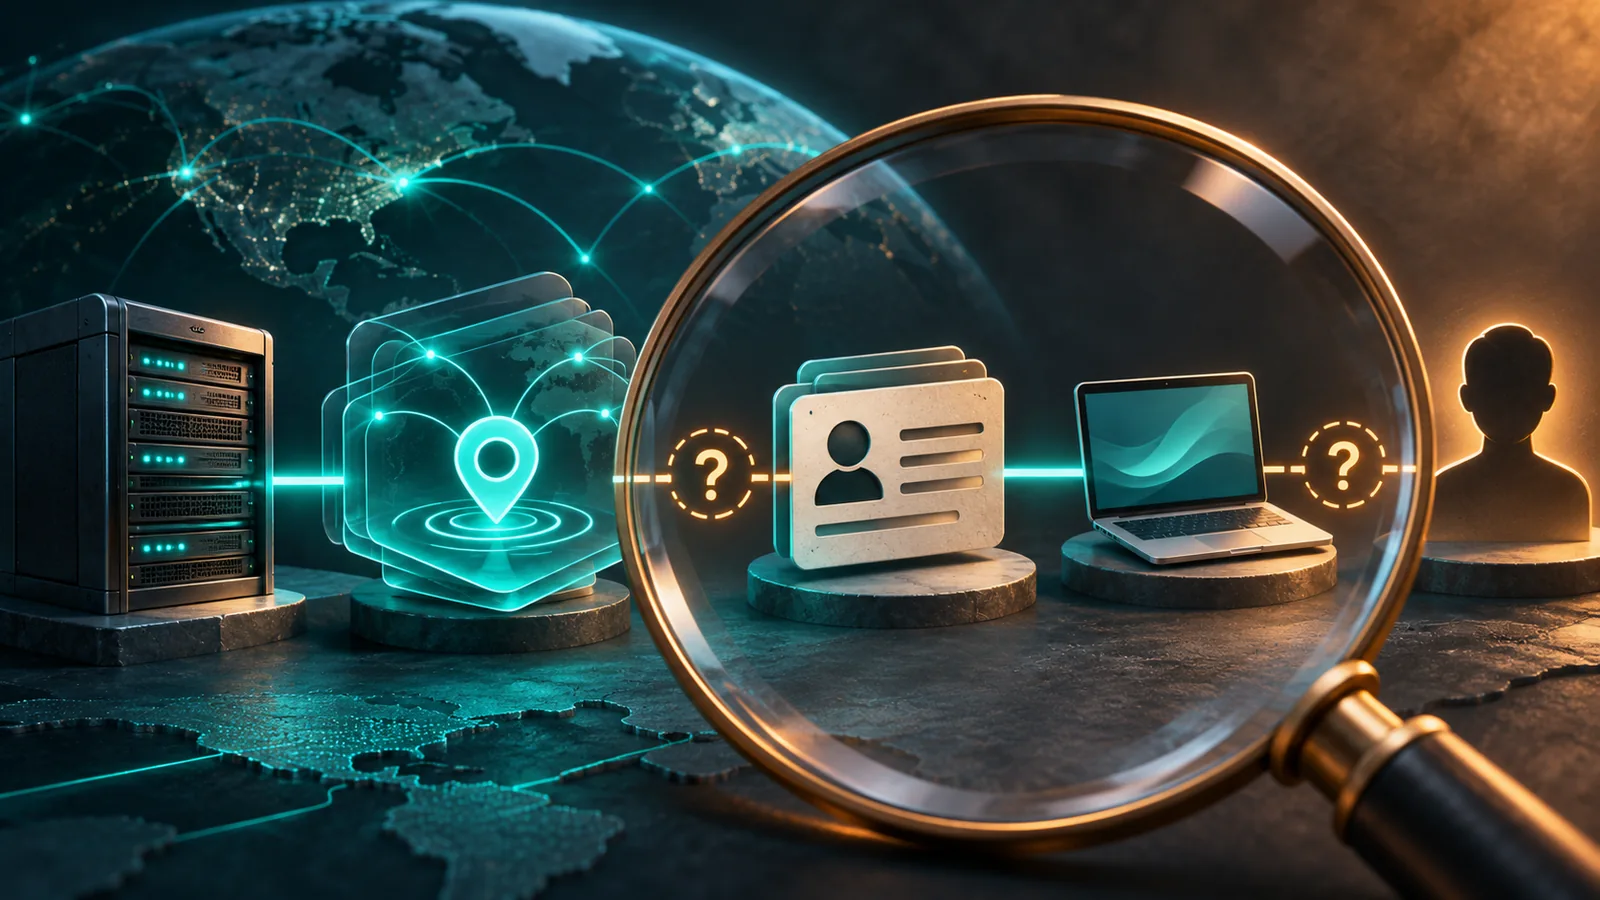
Follow the connection from observation to attribution
A VPN changes which systems can observe a connection. It does not remove all the information held by accounts, devices, payment services or the websites a person uses.
Different observations, different conclusions
| Subject | Possible information | What it does not prove |
|---|---|---|
| Website | VPN exit address, submitted account data | The subscriber behind that address by itself |
| ISP | Connection to a VPN endpoint | Every page visited inside the tunnel |
| VPN operator | Data available under its actual design and retention practices | That every provider stores full browsing history |
| Account or device | Logins, messages or local records if available | That VPN encryption was broken |
Trace the evidence chain one step at a time
From exit address to subscriber
Imagine a website records a VPN exit address at a particular time. That observation points to an endpoint used by the VPN service. To connect it to a subscriber, investigators would need further evidence that distinguishes the relevant connection from other traffic. Whether that evidence exists depends on the records and systems involved.
From subscriber to a person’s conduct
Even a subscriber association is not automatically proof of who was using a device or account at that moment. Shared devices, account access and the meaning of timestamps can become evidentiary questions. This hypothetical chain explains why an exit address, a subscriber identity and proof of conduct should be assessed as separate steps.
Can police ask a VPN for logs?
Authorities may seek records through applicable legal processes. Whether useful records exist depends on what the provider collected, how long it retained them and the systems involved. A request is not evidence that an identity match was possible or made.
Distinguish activity logs, connection metadata, subscriber details and billing records. Calling all of them logs hides important differences. Avoid claims that most VPN identifications follow one method unless reliable comparative data supports that claim.
Evidence can come from outside the tunnel
Signing into an account gives that website account information regardless of the public IP address it sees. Data stored on an accessible device or held by a recipient is another possible source.
These routes do not require an investigator to decrypt every VPN packet. Conversely, the possibility of such evidence does not mean it exists for every person or investigation.
What does no logs establish?
Read the policy’s scope and date. A statement about browsing activity does not necessarily describe account administration or every third-party service. An audit also has a defined scope and review period.
EFF explains the trust shift involved in using a VPN, and the FTC recommends evaluating the app and provider. Treat marketing as a claim to assess, not proof of a universal anonymity guarantee.
Ask what each privacy claim actually covers
- A provider may make separate claims about traffic content, connection timestamps, source addresses, payment details and support records. Read each category on its own. No browsing-history logs is narrower than no information about any customer, and a policy applying today does not by itself describe a past investigation.
- Also distinguish a policy promise from technical architecture and an independent review. A review can examine particular systems during a defined period; it does not make every possible future event impossible. The useful privacy question is which records a provider can hold and which observations remain elsewhere, rather than whether a single no-logs label settles all investigative scenarios.
What a documented operation can show
The DOJ’s account of an international disruption of a VPN service demonstrates that providers and infrastructure can themselves become investigative targets. Its specific facts should not be generalized to every commercial VPN or every lawful user.
A useful assessment asks what was observed, what records were available and how an attribution was supported. VPN use, attribution to a subscriber and proof of a particular person’s conduct are separate conclusions.
Questions people ask
Sources
Further reading
Glossary
Terms in this guide
Continue learning