Can the FBI Track Tor? What Investigations Actually Reveal
Yes, the FBI can sometimes identify a person who uses Tor. That does not mean it can trace every Tor connection or routinely decrypt the network. Identification can come from a compromised device, a controlled website, account records, financial evidence or other investigative leads. Assess the method and evidence in each case: observing Tor use, linking an activity and identifying a person are different achievements.
Understanding the question
Separate network visibility from personal attribution
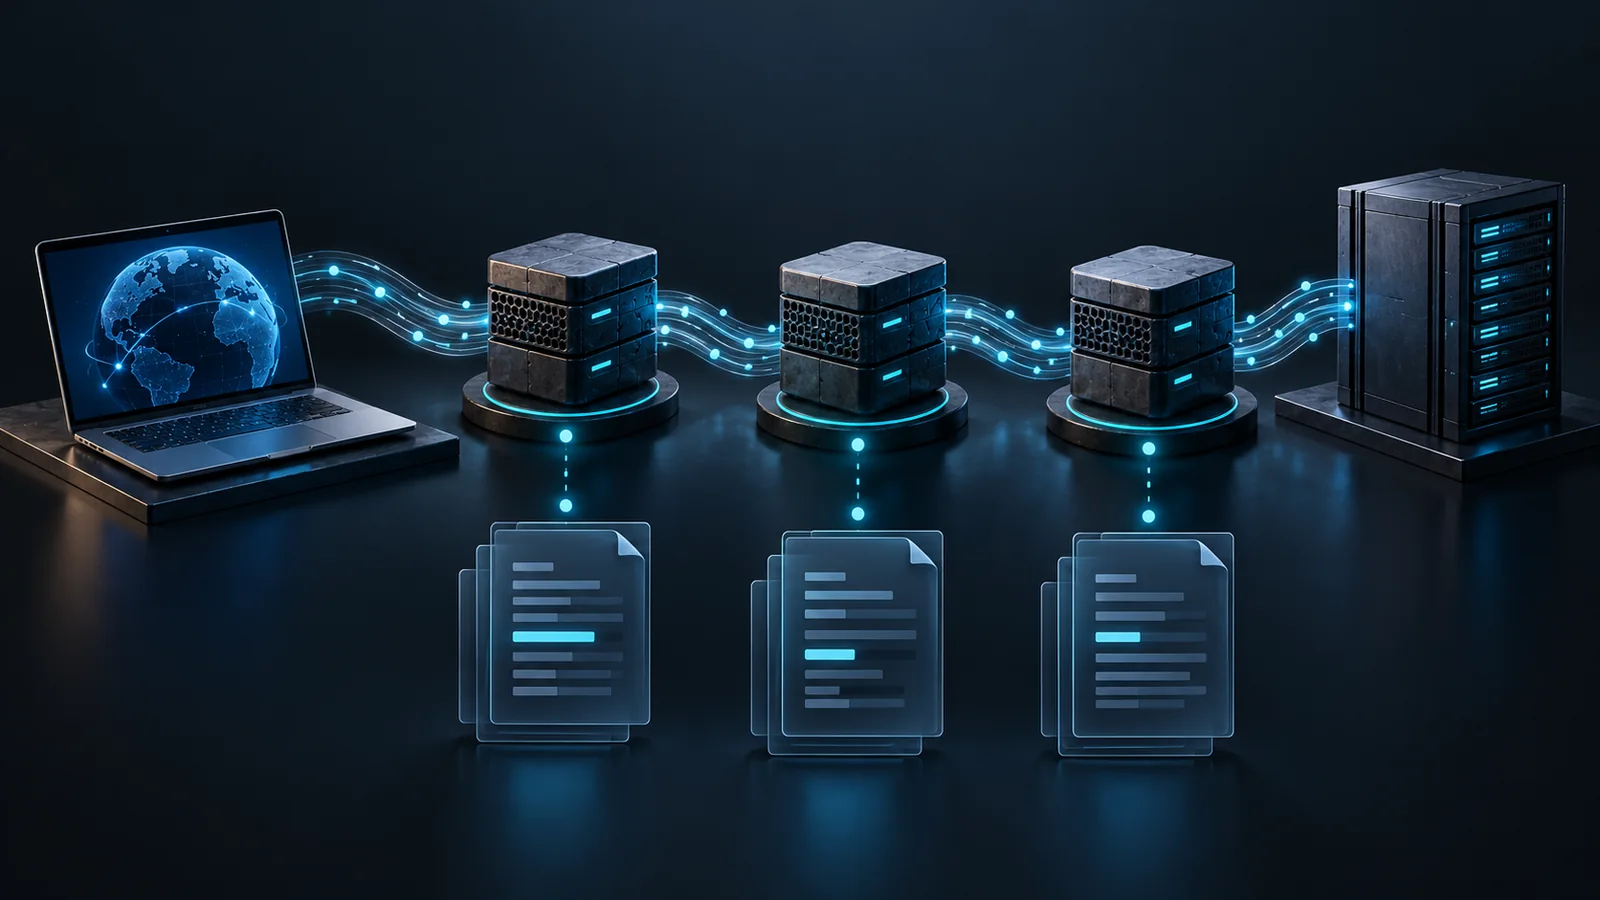
Tor separates the source and destination across relays. For an ordinary public website, traffic normally travels through a guard, middle relay and exit. The website sees the exit address; the guard sees the source connection. Onion services use a different rendezvous design, without a public-web exit.
An investigator may obtain information from the website, device or records outside that path. A real-world identity is a conclusion supported by evidence, not a field automatically supplied by Tor.
What the evidence establishes
| Subject | Assessment | Basis | Limit |
|---|---|---|---|
| Targeted identification | Strongly documented | Playpen NIT court records and official investigative account | Specific endpoint operation; not every connection |
| 2014 relay-early episode | Documented attack; incomplete attribution picture | Tor technical advisory; later CMU allegations are a separate source | Do not equate every affected descriptor lookup with a proven page visit |
| Universal decryption or tracing | Unverified by the records used here | No source here establishes an all-user capability | Unknown capabilities remain unknown |
The network attack that complicates the answer
The July 2014 relay-early episode belongs near the beginning because it concerns the network itself. Roger Dingledine’s July 30 advisory describes relays that modified protocol headers to link onion-service descriptor activity with source connections. Tor removed the identified relays on July 4 and released a fix for that particular vulnerability. This was more specific than the everyday statement that a website can recognize an account.
The advisory also limits the finding: a descriptor lookup was not proof of which application pages were loaded. The technical incident and the later claim about FBI payment to Carnegie Mellon are different evidentiary questions. Tor’s November 2015 post made the payment allegation; this review does not treat that post alone as independent proof of the amount or contractual arrangement.
This changes the answer from “it is always just a user mistake” to “network attacks also belong in the threat model.” It still does not establish general decryption of Tor’s layered encryption or an identity lookup for all users. The mechanism and the population affected matter more than the dramatic shorthand “Tor was broken.”
What an observer can learn from a connection
An ISP can ordinarily observe a connection to a known public Tor relay, with timing and volume. That alone does not reveal a destination page. A relay operator has a local circuit view rather than an ordinary end-to-end identity map.
For public-web browsing, an exit observes connections toward a destination. HTTPS protects application contents between browser and website; Tor alone does not provide that last-hop protection for HTTP. The destination receives the request and any information submitted to it.
Who Can See What?
Ordinary public-web use. Onion services have no public exit; active compromise and multi-point observation change these assumptions.
| Subject | Ordinary visibility | What that does not establish | Additional assumption needed |
|---|---|---|---|
| ISP | Subscriber connection to a public guard; timing and volume | Destination page or person at device | Further logs, endpoint or correlation evidence |
| Entry / guard | Source IP and next relay | Ordinary destination history | Additional observation or attack |
| Exit | Public-web destination; unencrypted HTTP if used | Original source IP | A separate linking method |
| Destination website | Exit IP, requests, submitted information | Source IP purely from routing | Identity disclosure, compromise or other evidence |
| Tor Project | Software and public network information | A central identity-to-destination map | No universal tracing facility offered |
| Investigators | Targeted evidence available in a case | Automatic knowledge of every user | Access, collection and corroboration |
Accounts and external records can provide the identifying link
An account may have a real email address, recovery telephone number, purchase history or earlier direct sign-ins. Using it through Tor can conceal the new network origin while leaving the service able to recognize the account. It does not erase records the provider already holds.
Investigators can connect service records with communications, financial information, physical evidence and interviews. A shared address, shared account or recycled username can mislead if treated as conclusive. Attribution should distinguish an initial lead from independently supported identity evidence.
Endpoint compromise changes the problem
A vulnerability can permit code to obtain identifying information on the originating device. Conceptually, this reaches the computer at the edge of the protected path. It is different from reading an identity out of Tor encryption.
The historical existence of such methods does not establish that a particular technique works against a current browser. A lack of public detail also does not prove that a capability is absent. Public records describe identified operations rather than a complete inventory of agency tools.
Playpen: a documented method with a narrow conclusion
The FBI describes its 2015 Operation Pacifier investigation as involving a court-approved Network Investigative Technique that obtained IP addresses and other information. Court records discuss the warrant and controlled website. This is a concrete example involving the destination and endpoint.
It does not show that an arbitrary user can be identified merely by launching Tor Browser. The operation involved particular infrastructure, software behavior and authorization. Separate documented history from speculation about current exploit coverage.
AlphaBay: infrastructure and international cooperation
The Department of Justice announced AlphaBay’s seizure in July 2017 and described cooperation among authorities in multiple countries. Infrastructure, accounts, assets and people can fall within different jurisdictions. Coordination assembles evidence that no individual relay possesses.
A seizure announcement establishes an operation and the agencies’ account. It is not a protocol analysis proving how every user was identified. Avoid assuming a market takedown means the anonymity network was decrypted.
Traffic correlation requires useful observations
A capable adversary may compare timing and volume at different points to test whether streams correspond. This operates on metadata without necessarily decrypting contents. It does not require owning every relay: strategically placed observations can matter more than node counts.
Tor acknowledges traffic-analysis limitations. Outcomes depend on visibility, duration, network conditions and alternative explanations. A proposed correlation is an inference requiring validation, not a universal lookup service. This guide cannot estimate whether an unspecified person is being observed.
Must investigators control every relay?
No. Counting relays alone misses two different routes to identification. Useful observations at separated points can support a correlation attack; access to a device or account can provide identifying evidence outside the circuit entirely. Neither route requires an investigator to own every relay in the network.
The hard question is what a particular observer could see and whether the proposed match survives alternative explanations. A shared network address or a timing resemblance needs context. Ask for the actual method and corroboration instead of choosing between the absolutes “all nodes must be compromised” and “everyone is already tracked.”
Does adding a VPN settle the issue?
No. It changes who sees the first connection and introduces another operator and configuration to trust. It cannot remove an account’s identity or sanitize a compromised device. The Tor Project generally does not recommend combining a VPN and Tor unless the user understands the configuration.
Choose tools against a defined privacy need, such as reducing exposure to local observation. An additional subscription is not an anonymity guarantee.
How to read an identification claim
Ask what was observed, what was inferred and what was proven. Did an agency identify a server or a person? Did a record show a subscriber address or establish who was at the keyboard? Was a technique described in a court record or only guessed at afterward?
These distinctions prevent both complacency and unnecessary alarm. Success against a particular target should inform threat assessment without becoming a claim that every Tor connection is exposed.
Claims this review cannot resolve
The sources used here do not establish a complete mapping from the 2014 relay attack to particular arrests, the full dataset retained, or a present-day successor operation. They also do not provide a current inventory of FBI tools. Those gaps should remain explicit rather than being filled with either a universal tracing claim or a universal safety claim.
Playpen is included as an endpoint example; AlphaBay is included as a platform-investigation example. Neither is treated as proof of a network-wide cryptographic break. Operation Onymous is relevant historical context, but a seizure announcement by itself does not disclose a complete technical identification method, so it is not used here to establish one. Intelligence-surveillance stories likewise cannot substitute for evidence about a particular FBI operation.
The browser-specific companion explains the endpoint boundary in greater depth. The wider dark-web investigation article follows how service access and external records can produce an identity even when the relay path is not traced. Keeping these questions separate makes both the documented successes and the unresolved limits easier to assess.
FAQs
Questions people ask
Sources
Further reading
- About Tor Browser
- Tor Project: HTTPS encryption and Tor
- Tor Project: why it cannot trace users
- Tor Browser best practices
- DOJ: AlphaBay seizure and international cooperation (2017)
- Federal court order: the Playpen NIT warrant
- FBI: Operation Pacifier and Playpen (2017)
- Tor Project: attacks remaining against onion routing
- Original discussion: how much anonymity Tor provides
- Tor Project: using Tor with a VPN
- Roger Dingledine, Tor Project (July 30, 2014): relay-early technical advisory
- Roger Dingledine, Tor Project (November 2015): CMU and payment allegations