Tor vs I2P vs Freenet: Privacy and Anonymity Compared
No network is always the most anonymous. Tor, I2P and original Freenet address different tasks and adversaries. Tor supports public-web browsing and onion services; I2P emphasizes communication inside its network; original Freenet, now Hyphanet, focuses on distributed publishing and storage. The newer project using the Freenet name is separate. Choose by the activity, application and observer you need to protect against, not an invented anonymity score.
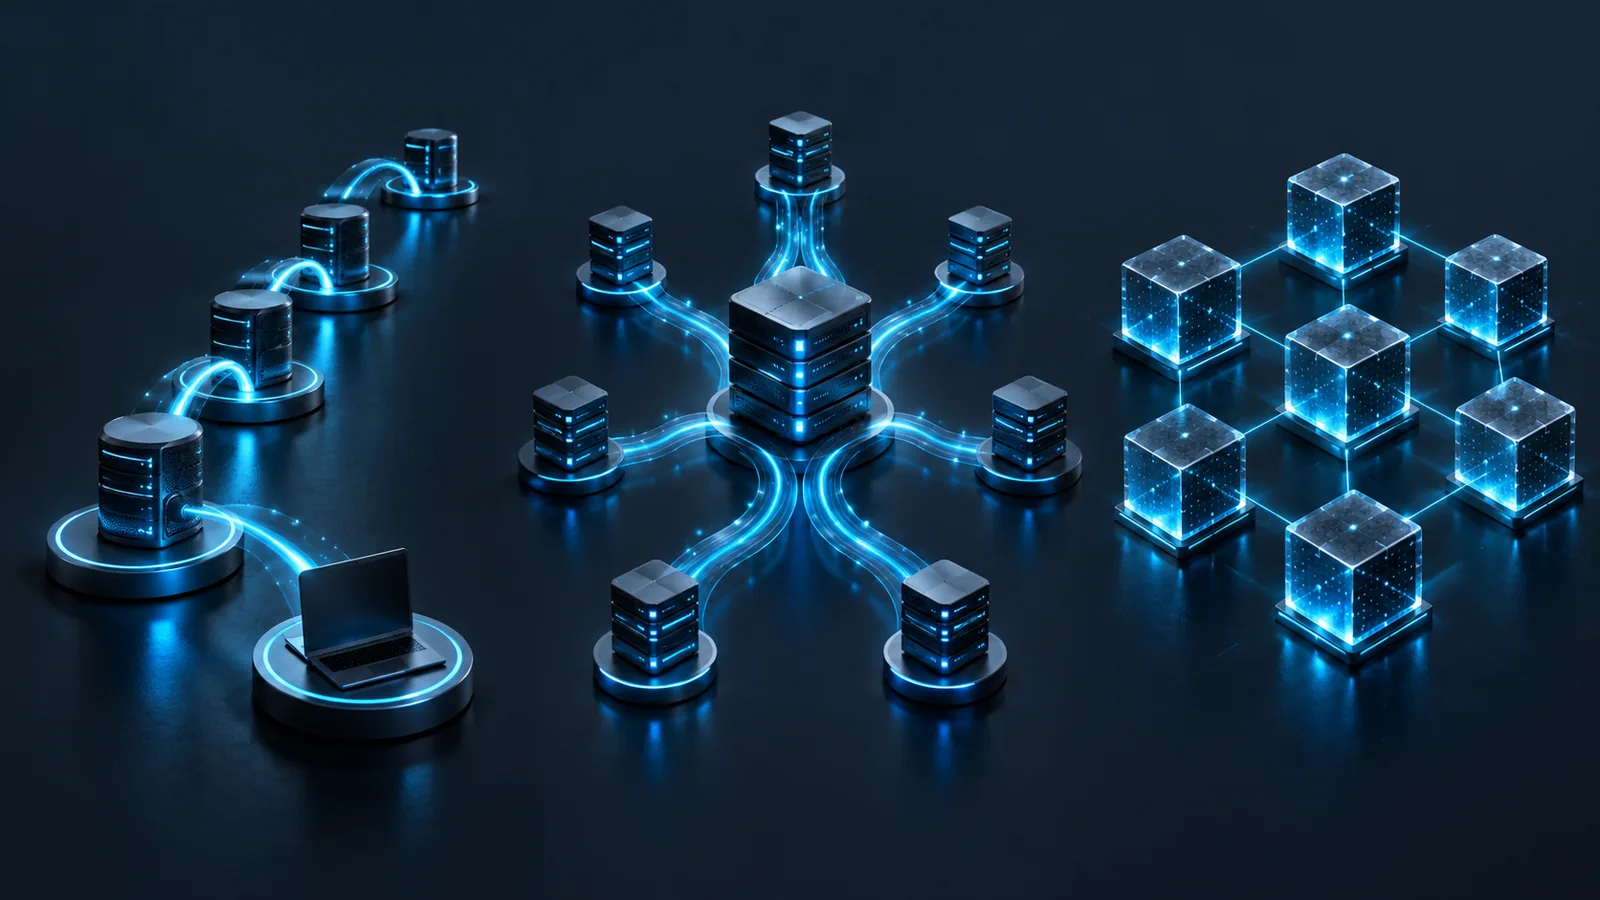
Understanding the question
First resolve the Freenet naming problem
Older comparisons use Freenet to mean the long-running encrypted storage and publishing network. That project continues as Hyphanet. The separate project formerly called Locutus now uses Freenet and describes a peer-to-peer platform for decentralized applications. Claims about one cannot automatically be transferred to the other.
This comparison uses Hyphanet for the original system. It discusses the newer Freenet separately and does not imply that decentralized applications automatically provide the same origin anonymity as Tor or I2P.
Tor: relay circuits for interactive connections
Tor routes traffic through relays to separate source and destination. For public websites, an exit connects to the ordinary internet. Onion services use a rendezvous arrangement without a public exit. Tor Browser adds browser-level privacy protections that a generic proxy configuration does not necessarily reproduce.
The distinction between browsing ordinary websites and accessing internal services matters. An exit sees a public-web connection’s destination side; HTTPS protects application contents on that hop. Merely counting layers cannot express every privacy property of a complete application.
I2P: tunnels and applications inside a network
I2P documentation describes an anonymous network layer supporting applications such as websites, messaging and file sharing. Its architecture uses separate inbound and outbound tunnels and a network database for routing information. Users run routing software, while application configuration determines what traffic actually uses it.
Public-web access through outproxies is distinct from I2P’s internal services and should not be assumed to have identical availability or trust assumptions to Tor exits. A network-layer tool also does not automatically normalize a browser’s fingerprint. The application remains part of the privacy assessment.
Hyphanet: distributed encrypted storage and publishing
Hyphanet routes requests through participating nodes and stores encrypted data chunks contributed by users. Content availability depends on the storage system, demand and caching behavior rather than a simple live connection to an origin website. That is a different design goal from proxying a visit to a public news site.
Its documentation distinguishes connections to known peers in darknet mode from more open participation. Here darknet is a connection-mode term, not a claim that every publication is illicit. Peer selection and knowledge of social relationships introduce assumptions that a three-column popularity ranking would miss.
The newer Freenet is a separate comparison
Hyphanet’s renaming notice explicitly separates the original project from the project formerly named Locutus. The current Freenet website describes serverless peer-to-peer applications and promotes a chat application. That identity and product direction were checked during this review.
Do not reuse an old claim about original Freenet’s storage anonymity as a guarantee for a newer Freenet application. Conversely, a feature or limitation in the new project says nothing automatically about Hyphanet. Evaluate the particular application, routing design and release documentation rather than relying on a shared historical name.
Architecture and use-case comparison
Functional comparison rather than a universal security ranking.
| Subject | Main purpose | Public websites | Internal model | Important limitation |
|---|---|---|---|---|
| Tor | Interactive network privacy and onion services | Supported through exits | Relay circuits; onion rendezvous | Traffic analysis and endpoint disclosure remain relevant |
| I2P | In-network communication and applications | Outproxies, not the core purpose | Separate inbound / outbound tunnels | Application setup and routing assumptions matter |
| Hyphanet (original Freenet) | Censorship-resistant publishing and storage | Not an ordinary web exit service | Encrypted distributed storage and request routing | Availability, peer relationships and application behavior differ |
| New Freenet (formerly Locutus) | Decentralized application platform | Not equivalent to a Tor Browser replacement | Peer-to-peer applications; consult current design | Do not assume historical Freenet anonymity properties |
Threat models determine which differences matter
Name the observer and desired secret. A local network operator, destination website, malicious peer, compromised device and observer with multiple network vantage points do not have identical capabilities. Also specify whether you want to conceal a reader, publisher, account identity or communication relationship.
For example, network privacy cannot hide identifying text you deliberately send. Distributed storage cannot ensure an infected operating system keeps a draft private. Browser protections cannot prevent a service recognizing an existing account. These are different layers, so evaluate the complete workflow instead of assigning the network a single score.
Is a bigger network automatically more anonymous?
More potential users can increase the set in which activity might blend, but a headline user count is not a measure of effective anonymity for one action. Reachability, routing, malicious participation, observation and application behavior affect which users are plausible alternatives.
Counts from different projects are also difficult to compare: clients, routers, connected peers and daily users are different measurements. This article does not offer current population estimates or infer an anonymity ratio from incompatible metrics. A comparison needs a common measurement and explicit assumptions.
Latency and usability are part of the security tradeoff
Interactive browsing needs timely responses, while a storage-and-publishing system can have different retrieval behavior. Router setup, application integration, available services and troubleshooting can matter as much to a lawful user as an architecture label.
There is no controlled performance benchmark in this review. Speed varies with routes, load, service availability and device configuration. A claim that one network is always faster or slower would need a reproducible workload and conditions. Usability problems also matter if they lead a person to bypass the tool for part of the task.
What real users ask: which network wins on paper?
What people discussed: The comparison thread asks whether another design would beat Tor with an equal population. Replies offer conflicting rankings, question the Freenet naming and ask whether the goal is internal services or the public web.
What the evidence says: The projects serve different workloads. Naming and application scope must be resolved before comparing anonymity; the thread’s unsupported compromise and ranking claims are not adopted.
Practical takeaway: Choose a task and adversary first, then compare the relevant documented properties.
Choose by Use Case
Lawful research and communication scenarios; a starting point is not a guarantee.
| Subject | Reasonable starting point | What to check first |
|---|---|---|
| Read a public website with network-origin privacy | Tor Browser | HTTPS, account identity and device security |
| Use or research I2P-native applications | I2P | Application routing, internal service and peer assumptions |
| Study resilient distributed publishing | Hyphanet | Storage, content availability and connection mode |
| Explore decentralized applications using current Freenet | New Freenet | Actual app privacy design; historical guarantees do not transfer |
| Protect a sensitive publication workflow | No universal answer | Source, editor, device, metadata and legal context together |
Maintenance status and documentation limits
The official Tor support site, I2P documentation, Hyphanet site and current Freenet site were accessible at review. I2P’s architecture page says parts originate in older work and marks its transport and cryptography sections current as of January 2025. A project-authored comparison also reflects that project’s perspective.
Those observations support consulting maintained official resources, not declaring a software version current indefinitely or certifying the absence of vulnerabilities. No release-by-release audit, penetration test or direct benchmark was conducted. Check release notices for the exact software you intend to use.
Keep application anonymity separate from network choice
Before relying on any option, check which program sends each connection, what identifiers it supplies and what the receiving service stores. A privacy-preserving transport can carry an identifying login. A file downloaded privately can later be opened in a different application.
The useful conclusion is therefore conditional: a tool can fit a particular task well when its protections and boundaries match your needs. That is more defensible than selecting a permanent winner based on network size, architecture names or anecdotes.
FAQs
Questions people ask
Sources
Further reading
- About Tor Browser
- Tor Project: HTTPS encryption and Tor
- Tor Project: understanding onion services
- I2P architecture and operation
- Hyphanet architecture, storage and connection modes
- Original Freenet renamed Hyphanet
- Current Freenet: peer-to-peer application platform
- Tor Browser best practices
- Tor Project: attacks remaining against onion routing
- Original discussion: comparing anonymity networks
- I2P project comparison: a project-authored perspective
- Tor Browser fingerprinting protections
Glossary
Terms in this guide
Continue learning